GitHub: receiving a security report and organizing its handling
A security report lacks version and reproduction. Learn how to organize the information, stay in touch, and choose who can read the GitHub discussion.
Category
A security report lacks version and reproduction. Learn how to organize the information, stay in touch, and choose who can read the GitHub discussion.
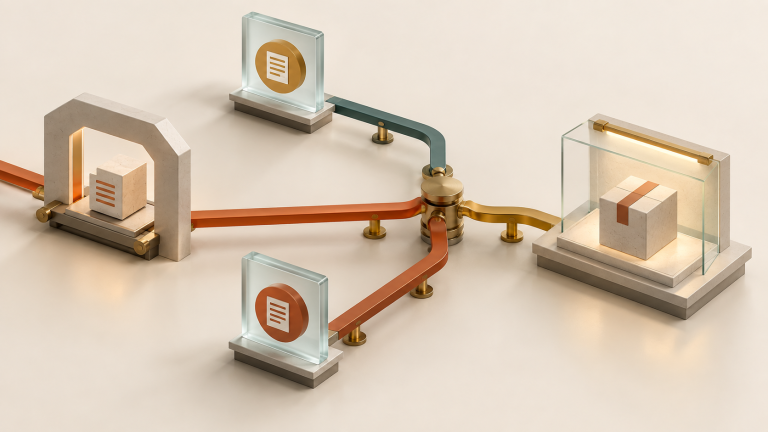
The first package requires coordinating creation, archive review, and pipeline identity. Follow the trust states and the 48-hour window, then prepare rejection tests without releasing an actual package.
Separate secrets, merge and npm publishing with GitHub rules and OIDC trusted-publishing configurations.
Copilot for JetBrains gains managed sandbox policies. Prepare a pilot that checks access, exceptions and actual enforcement of the rules.
The time between disclosure and exploitation of a vulnerability is shrinking, while validating a patch remains non-negotiable for critical applications. Here is how to limit exposure without confusing a temporary measure with remediation.
A prompt is not a security boundary. To allow an agent to modify a system, each write must be authorized, signed, isolated, and verifiable.